


Managed SOC 24/7: detection, analysis and response across your entire infrastructure
An in-house security operations centre in Spain that watches your endpoints, servers and cloud services, correlates every event in our SIEM and contains serious threats automatically, including at 3 a.m.
The IBERSYA SOC is a managed security operations centre that continuously monitors and correlates the security events of your endpoints, servers and cloud services. An analyst reviews every alert 8x5 and the platform responds automatically 24x7 —isolating the host, blocking the IP or blocking the mailbox— whenever there are serious signs of ransomware, intrusion or data exfiltration. It includes the Bitdefender GravityZone EDR licence at no extra cost, correlation in our own SIEM, external threat-intelligence enrichment of every alert, client access to our incident management platform and a technical and an executive report at the end of each month. Three service tiers from €6 per device/month, with an in-house SOC in Spain, direct contact with the technical team and all data held inside the European Union.
What the IBERSYA SOC includes in all three tiers
All three tiers share the same core —SOC, EDR and SIEM— and each higher tier adds another layer of visibility over the organisation.
Continuous monitoring
Permanent monitoring of endpoints and servers, extendable to network and email through telemetry add-ons.
EDR licence included
Bitdefender GravityZone deployed and licensed within the per-device price, in any of the three tiers.
SIEM and correlation
Every alert lands in our SIEM, which cross-references events across different machines and across different periods of time.
Threat intelligence
Before an analyst looks at it, each alert is enriched with external sources: we know whether that IP, domain or file already appears in known campaigns.
Active 24/7 response
Automated containment of serious threats in real time: host isolation and IP or email blocking with no prior validation.
Configurable notifications
We handle the incident, but you can receive an alert every time something happens in your organisation.
Incident platform
You access our platform with your own role and see only what is yours: your cases, their status and what we did about each one.
Monthly reports
A technical report and an executive report at the end of every month, one written for the IT team and one for management.
Baseline assessment
At kick-off we deliver an honest picture of the organisation’s security posture and of the vulnerabilities we found.
How the IBERSYA SOC works
All telemetry is centralised in a single SIEM. That is where a stray event becomes an alert with context, and where we decide what to do about it.
- Endpoints and laptops
- On-premise servers
- External attack surface
- Network traffic · add-on
- Email and identities · add-on
- Log and event collection
- Correlation in the SIEM
- Behavioural analysis
- Threat-intelligence enrichment
- Triage and prioritisation
- Real-time alerts
- Automated 24x7 containment
- Isolation and blocking
- 8x5 technical analysis
- Report and case closure
The path a threat follows, step by step
This is the real circuit of an incident, from the moment it reaches a client machine until it is neutralised and documented.
-
The threat arrives
An email with a malicious attachment, an infected download, a fraudulent website or an unauthorised connection attempt against a desktop, laptop or server running the EDR agent.
-
The EDR acts and sends telemetry
The agent blocks the threat if it can do so on its own and, whatever happens, sends all telemetry to our SIEM. That record is what later allows us to reconstruct exactly what occurred.
-
The SIEM correlates
The event is cross-referenced with what is happening on other machines and on previous days, and enriched with external threat intelligence before the alert is raised. An isolated attempt and a coordinated campaign stop looking alike.
-
Response
An analyst on 8x5 hours reviews the alert and rules out false positives. If it is real, we connect to the machine and neutralise the threat. If it is serious, the automated response acts 24x7 without waiting for anyone: it isolates the host, blocks the IP or blocks the mailbox.
-
Investigation
We determine the scope of the incident, its origin and the affected assets, and propose the measures needed to stop it recurring through the same route.
-
Closure and evidence
You get the notification if you have one configured, and the case is logged in the platform with every action taken, ready for the technical and executive report at month end.
Two response modes, one single defence
The platform responds automatically 24x7 to serious threats; analysis and case follow-up are carried out by an analyst on 8x5 hours. Machine speed with human judgement.
When the alert needs expert judgement
- Technical analysis: an analyst reviews every alert and determines the real scope of the event.
- Manual containment: remote connection to the machine to contain and neutralise the threat.
- Case management: every incident is documented in the platform and visible to the client.
On serious indicators, it acts on its own
- Automated detection: ransomware, unauthorised connections and exfiltration, in real time.
- Immediate containment: host isolation and IP or email blocking with no prior validation.
- All year round: cover at night, at weekends and on public holidays.
Three tiers of managed protection
Priced per device per month, whether server or endpoint. Common core across all three tiers: SOC, EDR and SIEM.
6 €
per device, per month
- Bitdefender GravityZone EDR licence included
- Technical analysis of every alert on 8x5 hours
- Automated 24x7 response to serious threats
- In-house SIEM with event correlation
- Threat-intelligence enrichment
- Access to the incident management platform
- Monthly technical and executive report
8 €
per device, per month
- Everything in Tier I
- Continuous monitoring of domains and IP addresses
- Leaked credential detection
- Sensitive data published or up for sale
- Your real attack surface exposed to the internet
- Actionable alerts: what to change and what to shut down
12 €
per device, per month
- Everything in Tier II
- Wazuh agent deployed on every device
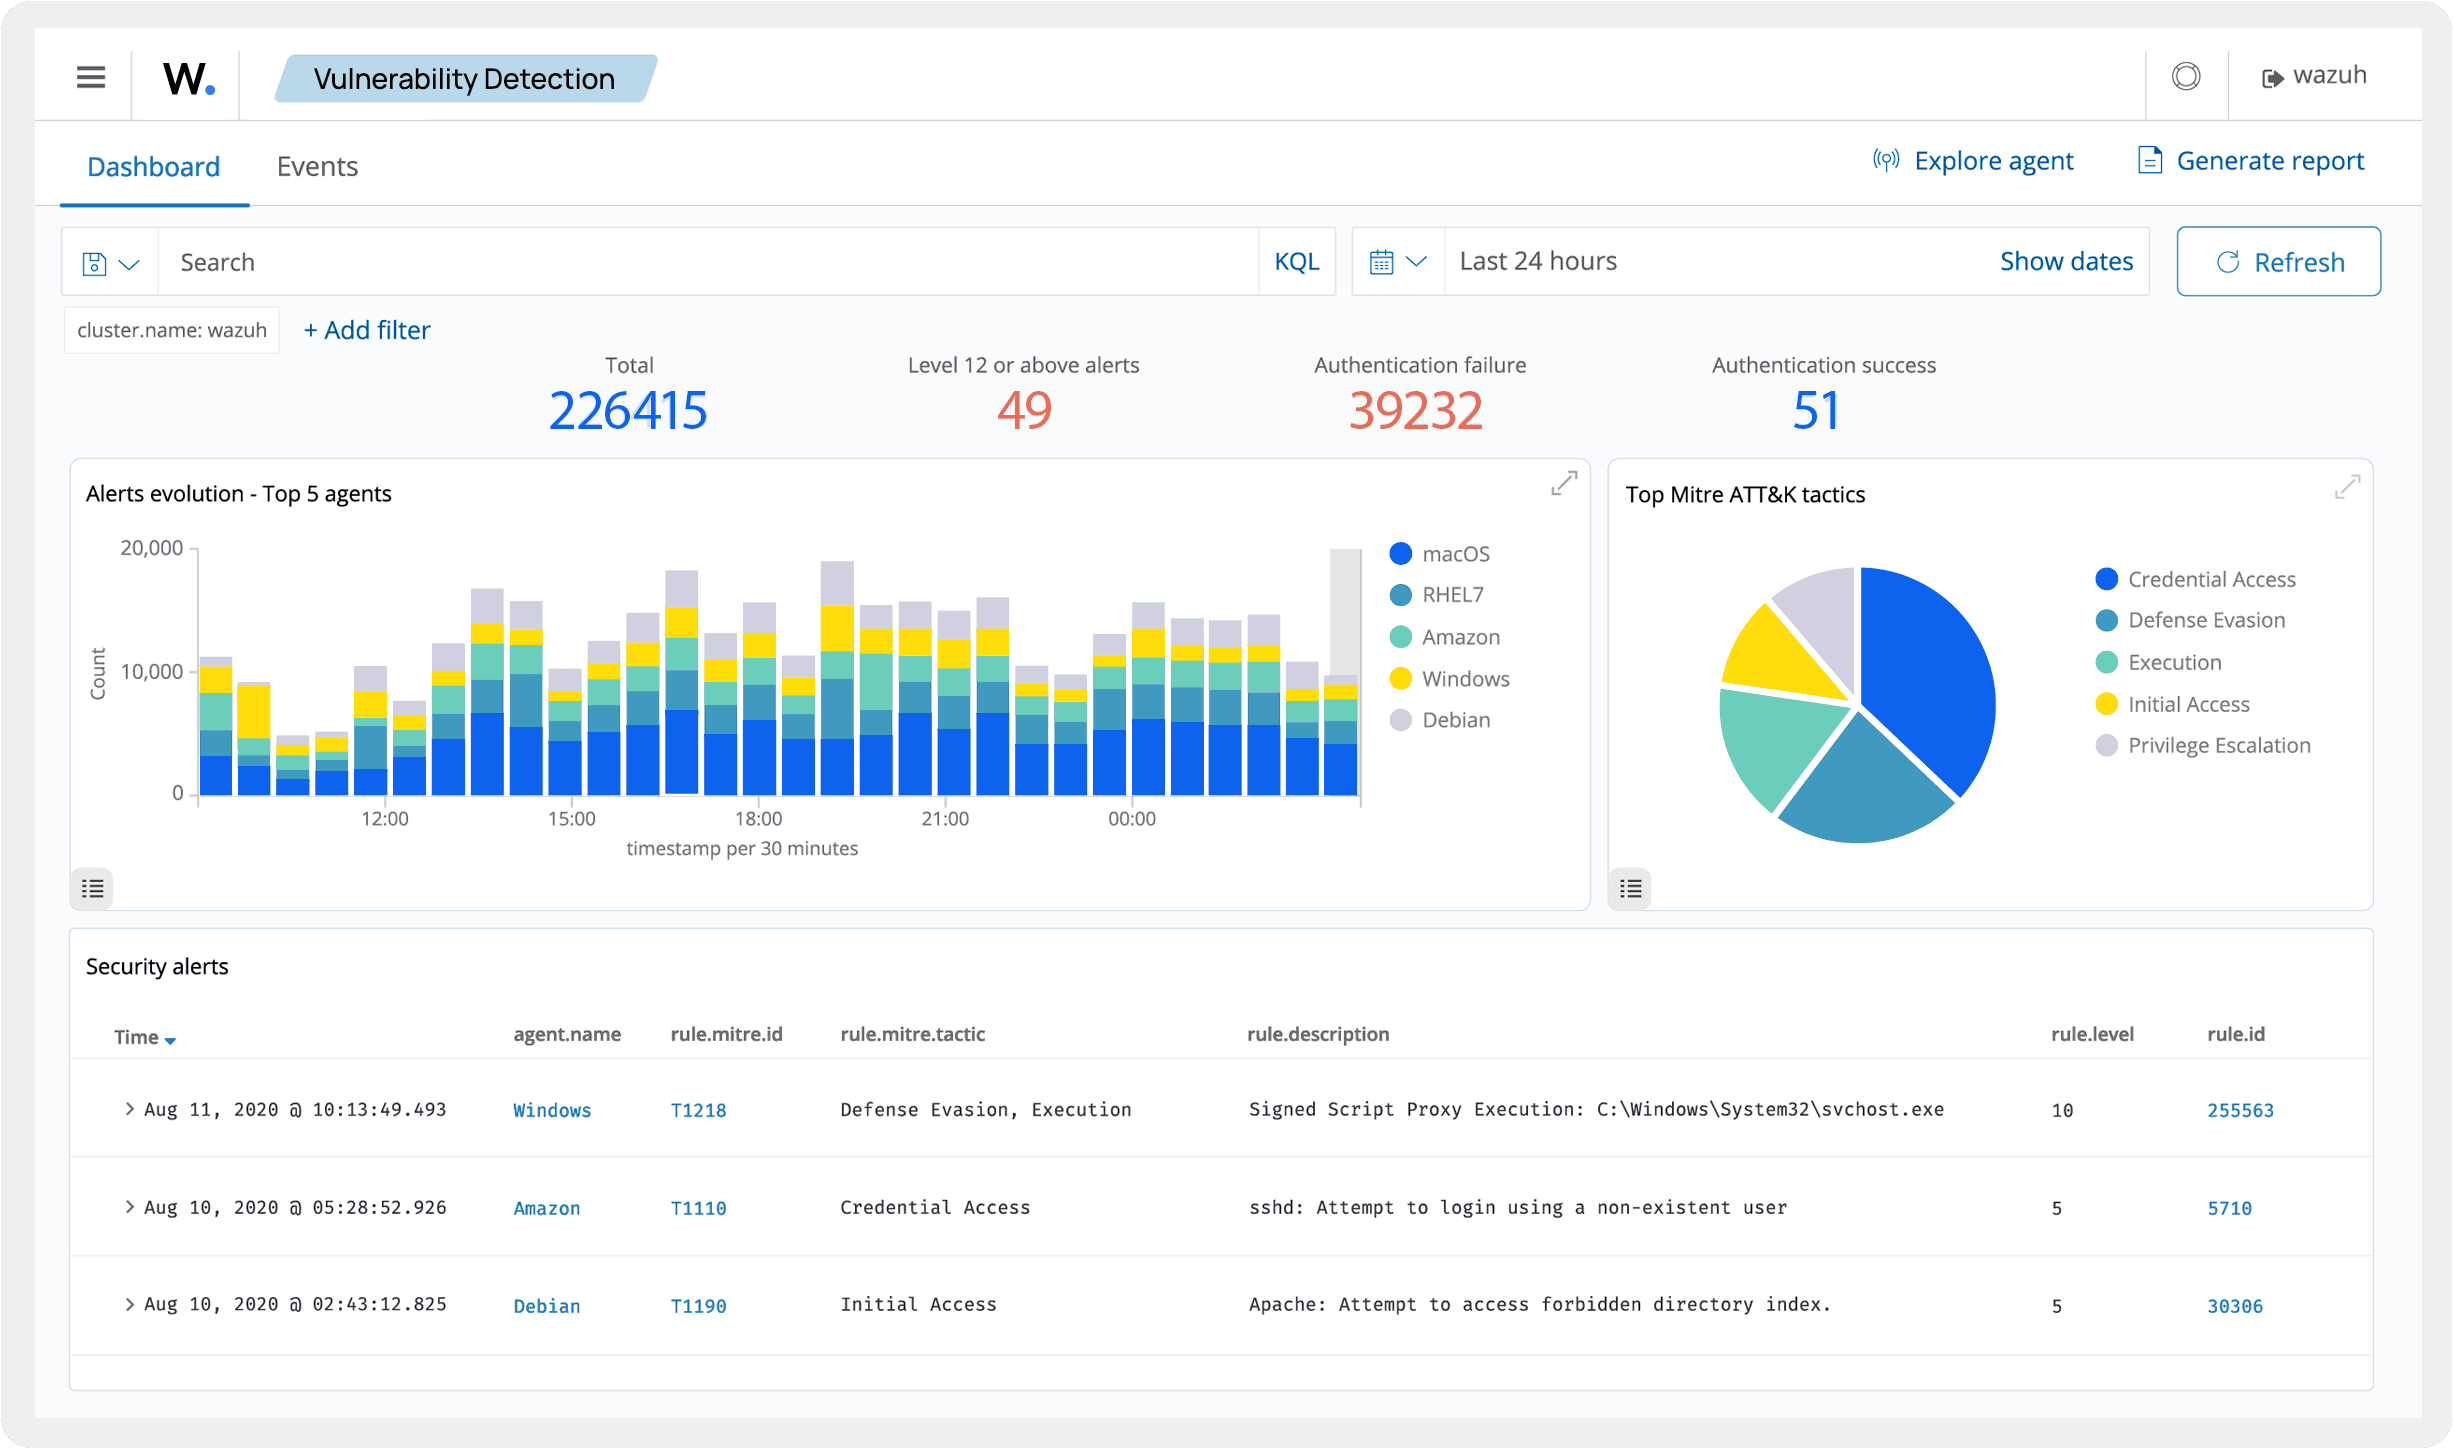
- Detection of outdated and vulnerable software
- Review of machine configuration and security policies
- Continuous inventory and sign-in history
- Direct evidence for NIS2, ENS and GDPR
Optional add-ons on any tier: Microsoft 365 telemetry (€60/month) and Fortinet telemetry (€60/month). The final figure depends on how many devices are monitored.
Two more sources for the same SIEM
Both sources join the rest of the telemetry and follow exactly the same alert, analysis and response path. They can be added to any tier.
Microsoft 365 telemetry
We collect your tenant telemetry to detect and stop attacks against user accounts and corporate email.
- Impossible travel: a user signing in from the Dominican Republic and five minutes later from Spain. The account is blocked immediately.
- Email security: phishing, impersonation and mailbox rules created behind your back.
- Critical changes: creation of Azure applications and sensitive configuration changes.
- Data leakage: alerts on mass downloads or data exfiltration.
Fortinet telemetry
We integrate your FortiGate firewall telemetry to watch everything happening at the network perimeter.
- Configuration changes: immediate notice of any firewall modification.
- Brute-force attacks: detection of repeated access attempts against the network.
- Suspicious sign-ins: monitoring of VPN and administrative access.
- C2 connections: traffic towards command-and-control infrastructure.
Is your business protected while you sleep?
Request a proposalCertified technology and official partners
Bitdefender GravityZone is the standard EDR included in the price. As official partners of CrowdStrike and Palo Alto Networks, the SOC can also operate on their platforms when the organisation has already made that investment or needs a specific stack because of a group or customer requirement.
Bitdefender GravityZone
The service’s standard EDR, licensed within any of the three tiers. Included
CrowdStrike Falcon
Premium EDR/XDR. We operate the SOC on Falcon and ingest its telemetry into the SIEM. Premium option
Palo Alto Networks
NGFW firewall and Cortex XDR. Perimeter and endpoint telemetry integrated into the SOC. Premium option
Fortinet FortiGate
Perimeter security and network telemetry available as a service add-on. Add-onOur SIEM is Wazuh, case management runs on IRIS, and indicator enrichment on MISP plus public threat-intelligence sources such as AbuseIPDB and AlienVault OTX. Where a deployment calls for it we work with products listed in the CPSTIC catalogue of the Spanish National Cryptologic Centre and aligned with the Spanish National Security Framework (ENS).
Regulatory compliance: NIS2, ENS, DORA and GDPR
A SOC provides the active controls and incident traceability that the main regulatory frameworks require. Non-compliance can carry fines of up to 2% of annual turnover.
NIS2
EU cybersecurity directive for essential and important sectors. Requires risk management, detection capability and incident notification.
ENS
Spanish National Security Framework, mandatory for the public sector and its suppliers. Requires monitoring and activity logging.
DORA
Digital operational resilience regulation for the EU financial sector. Requires detection, response and ICT incident reporting.
GDPR
Personal data protection: traceability, breach detection and notification within the deadline. The SOC supplies the evidence of control.
Client platform and monthly reports
We handle the incident, but the visibility is yours. You access our incident management platform with your own role and see only your own information: your cases, their status and the actions taken on each one. At the end of the month you receive two reports: a technical one for the IT team and an executive one written for management.
- Access with your own role: you only see your cases, their status and the actions taken
- Technical report and executive report at the end of every month
- Follow-up and log of the work carried out proactively
- Notification of the vulnerabilities found in your organisation
- Client folder in SharePoint with proposals, contracts and documentation
A guided, friction-free rollout
Response capability is live from the first phase. Initial deployment takes around two weeks.
Kick-off
We align objectives and collect the inventory of machines and servers to monitor.
Deployment
EDR agent installation and configuration of security policies tailored to you.
Baseline
We deliver the assessment document and the list of vulnerabilities found.
Operation
Continuous monitoring, contingency plan and monthly technical and executive reports.
Phases 1 and 2 · around 2 weeks
Why choose the IBERSYA SOC
What sets us apart from off-the-shelf antivirus, from a generalist IT provider and from a high-volume MSSP.
In-house SOC in Spain
The analyst who answers works at IBERSYA, with direct contact to the technical team. No ticket queues, and all data inside the European Union.
Genuine automated response
Immediate containment at night, at weekends and on public holidays too. Actions fire according to defined rules and are logged case by case.
Automated plus human
Machine speed to contain, analyst judgement to investigate. Filtering false positives is a large part of the job.
EDR licence included
Bitdefender GravityZone sits inside the per-device price at any tier. When comparing quotes, add up what the other provider bills separately.
SIEM correlation
We cross-reference events across machines and across time to catch attacks that, looked at in isolation, draw no attention.
Tiered model
You start at Tier I and move up when it makes sense. There is no need to buy the full package on day one.
SOC glossary
The terms that appear in any SOC proposal, explained without jargon.
- SOC
- Security operations centre: the team and platform that monitor, investigate and respond to incidents.
- SIEM
- A system that collects events from every machine and tool and cross-references them to detect attacks that would be invisible on a single device.
- EDR
- Advanced antivirus. As well as matching files against known threats, it watches machine behaviour and keeps a record of everything that happens.
- SOAR
- Response automation: rules that execute containment actions on their own, without waiting for an analyst to be at the desk.
- MDR
- Managed detection and response. It is the IBERSYA SOC service model: we provide both the technology and the analysts.
- 8x5 / 24x7
- Service windows. 8x5 means 8 hours a day, 5 days a week. 24x7 means any hour, every day of the year.
- Telemetry
- The data that machines and security tools send continuously about what is happening.
- False positive
- An alert that looked dangerous and turns out to be harmless on review. Filtering them is much of the SOC’s work.
- Containment / isolation
- Disconnecting a machine from the network so the threat cannot spread, without powering it off or losing the evidence.
- Attack surface
- Everything the business exposes to the internet that an attacker could try to use: website, email, remote access, IP addresses.
- Cyber intelligence
- Monitoring what happens outside the network: whether the company’s passwords, domains or data appear published or for sale.
- C2 (command and control)
- The server an attacker uses to issue orders to an already infected machine. Detecting such a connection means the machine is compromised.
- Impossible travel
- Two sign-ins to the same account from places so far apart the person could not have travelled between them. Almost certainly a stolen account.
- Ransomware
- Software that encrypts the company’s files and demands a ransom. It is the incident that most often stops a business outright.
Frequently asked questions about the managed SOC
What is a SOC and what is it for?
How much does a managed SOC cost for a business?
What is the difference between a SOC and just having antivirus?
How does 24/7 protection work if technical analysis is 8x5?
Does the SOC replace my IT provider or my in-house IT team?
What data of my company does the SOC see?
How long does the service take to go live?
Does the SOC help with NIS2, ENS, DORA or GDPR compliance?
Is there a minimum number of devices to sign up for the SOC?
Can you integrate CrowdStrike or Palo Alto Networks if I already have them deployed?
Request a managed SOC proposal
Tell us how many machines and servers you have, whether you use Microsoft 365 and whether you have a firewall. With that we can quote you and show you the platform in a demo.